Practical preparation / secure systems
Security engineering interviews: threat models, incident triage and verified fixes
Prepare for security engineering conversations with a threat-modeling workflow, secure-development evidence and original practice tasks for abuse, incident response and rollout verification.
- Start
- Name assets and actors
- Prioritize
- Impact × plausibility
- Finish
- Verify the control
Preparation map
Four moves before the interview
- 1
Choose a surface
Define the protected asset, legitimate workflow and relevant attacker capability.
- 2
Find abuse paths
Identify trust boundaries and specific failures rather than listing generic threats.
- 3
Choose controls
Balance prevention, detection, recovery and the cost imposed on users.
- 4
Prove the fix
Design tests, telemetry, a staged rollout and an incident review.
01 / FIELD NOTES
Anchor the interview to the security role
Application security, cloud security, product security, detection engineering and incident response ask for different depth. Read the live requisition before choosing your practice exercises.
- For an application-security role, prepare a code or design review showing a vulnerability, exploit path, fix and regression test. For detection work, prepare a signal, triage rule, false-positive analysis and investigation timeline.
- For cloud or platform security, explain identity boundaries, secrets, deployment controls and the trade-off between isolation and operational complexity. A list of vendor services is not a threat model.
- Ask the recruiter whether the round includes a live review, architecture case, incident scenario or behavioral discussion. Never assume a leaked question bank predicts the actual assessment.
- Use a project you can describe without exposing a former employer's systems. Make the protected asset, your decision, evidence and remaining risk visible.
02 / FIELD NOTES
Threat-model a concrete workflow
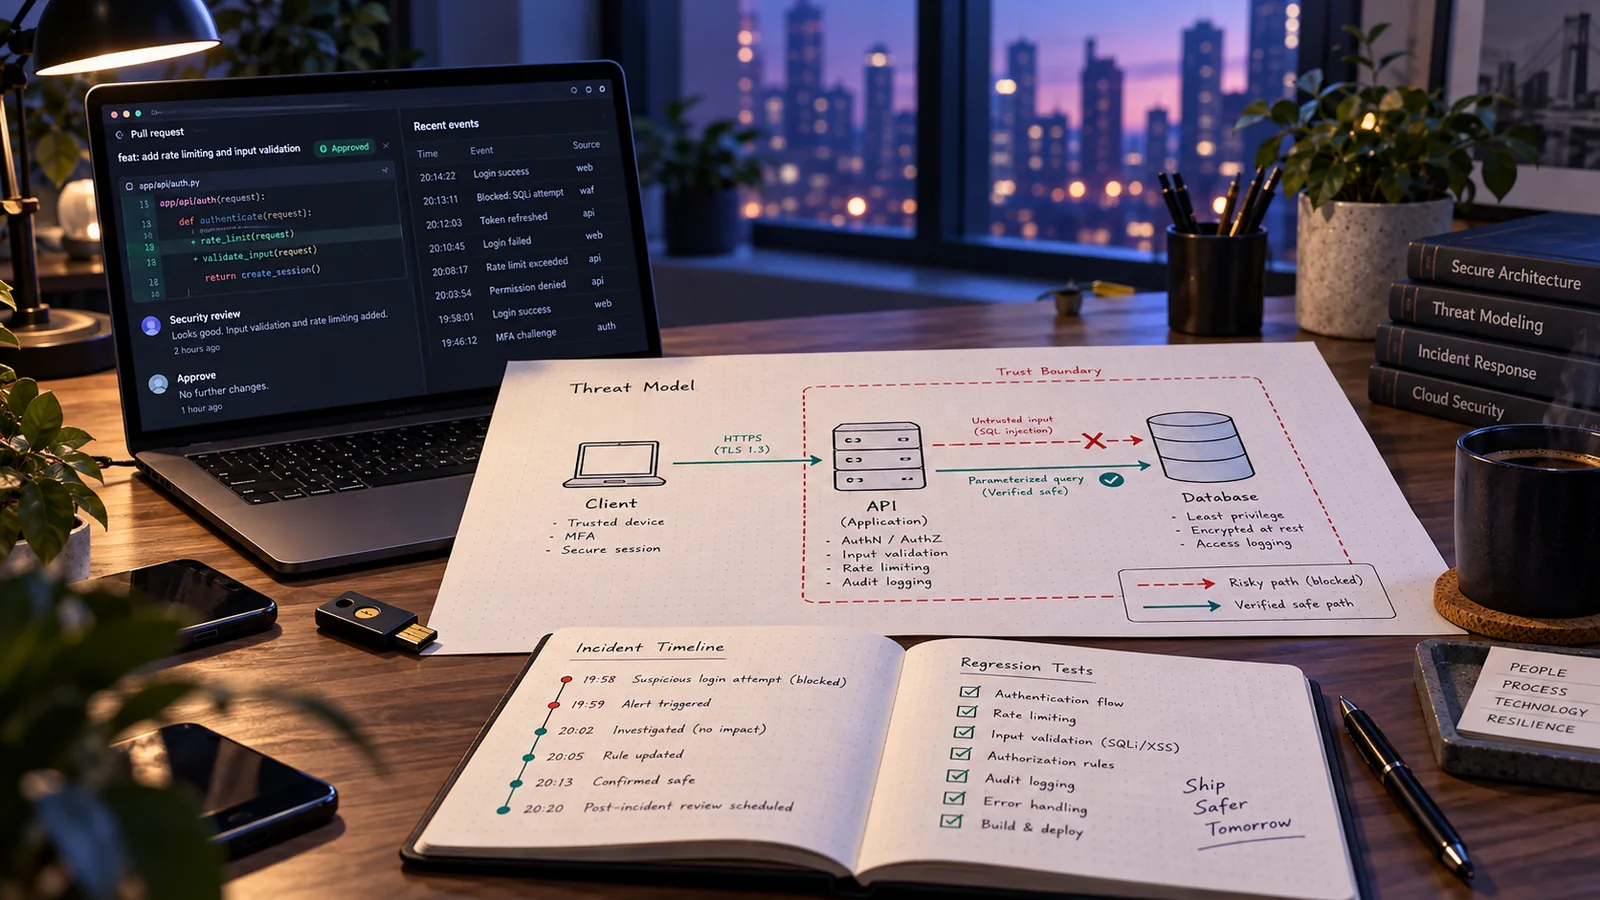
An effective answer follows the data and decisions a system makes. It should state what an attacker can control and what they cannot.
- Begin with a simple sequence: user request, authentication, authorization, service, data store and external integration. Mark trust boundaries and valuable data. Ask which operations are sensitive and who may perform them.
- Describe an abuse case in operational terms: an attacker with a low-privilege account changes an object ID and reads another tenant's record. Name the missing authorization check and the observed impact.
- Prioritize by plausible attacker access, impact and exposure. Do not claim to calculate a precise probability from a diagram. Explain what evidence would change your priority.
- Choose a control at the correct boundary. Validate authorization on every relevant request, use least privilege in the backend and add a regression test that fails before the fix.
03 / FIELD NOTES
Make secure development observable
The NIST Secure Software Development Framework organizes practices across preparation, protection, production and response. Use it to explain a real workflow rather than to recite section names.
- Show how a code review, dependency scan or automated test enters a release decision. A tool finding is not a confirmed vulnerability until a person or reproducible test establishes context and exploitability.
- Describe how secrets are issued, rotated and revoked. Avoid placing credential material in build logs or a public repository, even when the code is only a practice exercise.
- For a dependency incident, identify the deployed versions and reachable paths before declaring every service equally affected. Prepare a containment option and a fix that can be staged and rolled back.
- Keep detection and prevention separate. A log that reveals abuse later is valuable, but it does not replace a missing authorization check. Conversely, prevention without telemetry can hide an ongoing attack attempt.
04 / FIELD NOTES
Walk through response and learning
Interviewers often test how you behave when evidence is incomplete and the business is operating. A calm sequence is more useful than a heroic claim.
- State the first objective: preserve evidence, limit harm and keep the response coordinated. Identify an incident lead, a decision log and the signal that justifies containment.
- Separate confirmed facts from hypotheses. Ask which accounts, tenants, systems and time period may be affected. Avoid publishing a breach claim before evidence supports it.
- Choose containment proportional to impact: revoke a credential, block a vulnerable endpoint, restrict a permission or disable a feature. Explain the customer cost and how you will verify containment held.
- After recovery, add a regression test and an alert that would have exposed the issue earlier. Review why the original boundary failed and assign a clear owner to each improvement.
Original practice bank
Three tasks to work through aloud
These are ApplyDjinn practice prompts, not questions obtained from an employer. Use them to rehearse the reasoning and verification expected for the role.
Exercise 1
Cross-tenant document access
Prompt: A file API checks that users are signed in but accepts any document ID. Show the threat, a fix and how to know the fix works.
Approach: Model tenant identity and object ownership; enforce authorization at the data access boundary; use deny-by-default behavior and record access decisions without leaking document contents.
Test: Test a valid owner, a different tenant, guessed IDs, list and download routes, cached responses and a service account with broader permissions.
Follow-up: What would you do if an access log suggests the bug has existed for months?
Exercise 2
Compromised dependency
Prompt: A library used by several services is reported compromised. How do you prioritize investigation and rollout?
Approach: Verify the advisory, versions, code paths and deployed inventory; identify exposure; isolate or pin where appropriate; stage a replacement and keep evidence of the decision.
Test: Include a service that imports but never executes the vulnerable path, a transitive dependency and a fix that breaks a critical API.
Follow-up: When is temporary isolation safer than an immediate broad upgrade?
Exercise 3
Abusive login traffic
Prompt: Traffic to sign-in rises sharply while real users report slow logins. Design containment that does not lock out everyone.
Approach: Use source and outcome telemetry, rate limits with appropriate keys, bot signals and backend capacity controls; protect the password and passkey paths; give legitimate users a recoverable experience.
Test: Check distributed sources, shared IPs, false positives, credential stuffing, session creation load and cache expiry behavior.
Follow-up: How would you prove the limit helped legitimate-user latency?
Source check
Primary sources
These primary materials support the published process or technical context. The exercises and preparation framework are original editorial material; confirm your own interview format with the recruiter.
Continue preparing with evidence
Choose a current role, map its requirements to projects you can defend, then practice the round your recruiter actually scheduled.